Reducing cybersecurity risks before they impact business
Identify and manage threats early to prevent incidents, disruption and unnecessary costs.
Software development with end-to-end competence
Cybersecurity regulation is changing how organizations manage security and how digital products are developed and maintained.
Wapice helps you identify what applies, assess your current situation and turn compliance requirements into practical action.
Reducing cybersecurity risks before they impact business
Identify and manage threats early to prevent incidents, disruption and unnecessary costs.
Building trust and strengthening competitiveness
Demonstrate strong security practices and compliance to customers, partners and other stakeholders.
Making security processes more efficient
Standardized approaches such as ISMS and Secure Development Lifecycle practices help reduce errors, clarify responsibilities and improve everyday workflows.
Improving incident readiness and resilience
Strengthen your ability to detect, respond to and recover from cybersecurity incidents quickly and effectively.
Security compliance is no longer limited to information security teams or occasional audits.
New EU cybersecurity requirements affect organizational governance, risk management, incident response, supply chains and increasingly the products companies develop and sell.
For many organizations, the challenge is not a complete lack of security practices. The challenge is understanding what needs to change, what is already sufficient and how to demonstrate compliance efficiently.
The goal should not be compliance for compliance’s sake.
Well-designed security processes improve resilience, reduce risks and make security easier to manage as part of everyday operations.
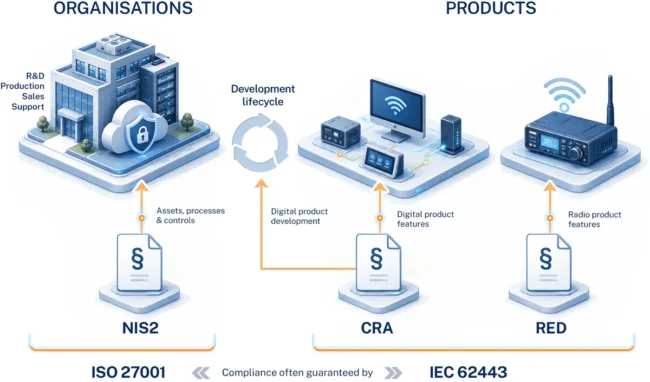
NIS2 directive creates a common cybersecurity framework with the aim to strengthen resilience against ever growing cyber threats. It expands the scope of information- and cybersecurity obligations via risk management, incident reporting, secure supply chains, vulnerability management and awareness.
ISO/IEC 27001 is the leading international standard for Information Security Management Systems (ISMS). It provides organizations of all sizes and industries with a framework to establish, implement, maintain, and continuously improve their information security practices. Achieving compliance with ISO/IEC 27001 demonstrates that an organization has a structured system in place to identify, manage, and reduce risks while following internationally recognized best practices.
NIS2 introduces a few precise requirements e.g., authority and incident reporting requirements, but many of its requirements are abstract. A strong method for proving NIS2 compliance is to certify for suitable security standards, especially ISO/IEC 27001. A well-establised ISMS provides a strong foundation for NIS2 compliance and makes the implementation significantly lighter, as the two frameworks are closely aligned.

Wapice has maintained an ISO/IEC 27001 certified information security management system since 2019, giving us first-hand experience of building and continuously improving systematic information security practices. Learn more >
Wapice helps organizations interpret NIS2 requirements and turn them into practical governance, risk management and compliance actions. Learn more >
Cybersecurity regulation increasingly affects not only organizations, but also the digital products they develop, sell and maintain. Security, compliance and risk management therefore need to be considered throughout the entire product lifecycle.
The Cyber Resilience Act (CRA) introduces mandatory cybersecurity requirements for products with digital elements sold in the EU. The requirements cover areas such as secure design, vulnerability management, security updates and incident handling throughout the product lifecycle. For product development organizations, preparing for CRA should therefore be a priority.
The Radio Equipment Directive (RED) includes cybersecurity requirements for certain types of connected radio equipment. The EN 18031 series provides harmonized standards that support conformity assessment for these requirements.
IEC 62443 is one of the most widely recognized cybersecurity standard families for industrial automation and control systems. It provides a structured framework for both secure product development processes and technical security requirements.
Standards such as IEC 62443 and EN 18031 can provide a practical way to interpret and implement regulatory requirements. Because CRA, RED and IEC 62443 all rely strongly on risk-based thinking, an efficient risk assessment process is key to achieving compliance without unnecessary complexity.
Wapice is IEC 62443 ready entity and consultant with an internal training and certification program on IEC 62443-4-1 and 4-2 for all developers.
Our experts can adapt the requirements to each organization’s tools and workflows while leveraging the standard to ensure security throughout the development and product lifecycle.
Wapice helps companies translate CRA and RED requirements into practical product development, risk management and compliance activities. Learn more >
Meeting EU cybersecurity requirements can also create a strong foundation for compliance and security assurance in other markets, reducing duplicated work when expanding internationally.

We combine compliance expertise with practical cybersecurity and engineering capabilities. This allows us to support you from initial assessment and planning to implementation and continuous improvement.
Cybersecurity regulation does not need to become a separate layer of bureaucracy.
When requirements are translated into practical processes and engineering practices, compliance can strengthen security, resilience and product quality at the same time.
Whether you are preparing for NIS2, developing an ISO/IEC 27001 compliant ISMS or getting your products ready for CRA, RED or IEC 62443, we can help you identify the right next steps and put them into practice.